

Cyber security consulting | Information-security consulting | Vulnerability management | VAPT | Security governance | Risk and compliance | Virtual CISO support | Privacy and data-protection consulting | ISO/IEC 27001 programmes | Cloud security | Application security | Network security | Security operations | Security audits | Security-policy development
Saarth Infosec Private Limited offers cybersecurity consulting, VAPT, information security advisory, Virtual CISO services, GRC, DPDPA readiness, and ISO/IEC 27001 consulting to organizations in Dahisar, Mumbai, and the surrounding business districts.
Modern businesses run on cloud applications, email, websites, APIs, remote access, digital payments, and customer data and every one of these touchpoints can become a security or privacy risk if it isn’t properly assessed and managed.
Saarth Infosec partners with organizations looking to understand these risks, strengthen their security controls, and build a structured information security programme not just patch things together with individual security products.
Cyber Security Company in Dahisar
Contact Saarth Infosec Private Limited
Website: https://www.saarthinfosec.com/
Phone: +91 8459122400 / +91 8390593233 / +91 8459670117
Email: success@saarthinfosec.com
Office Address: Office- #136, VTP Trade Park, near Star Bazzar, Shree Siddhivinayak Meera, Undri, Pune, Maharashtra 411060
Quick Business Information
Business Name: Saarth Infosec Private Limited
Service Category: Cyber Security & Information Security Consulting
Website: https://www.saarthinfosec.com/
Core Services: Cyber Security Consulting, VAPT, Virtual CISO, GRC, DPDPA Consulting, ISO/IEC 27001 Consulting, IT Security Consulting and Data Privacy Consulting.
Suitable For: Startups, SMEs, enterprises and organizations handling sensitive business, customer or employee information
Engagement Type: Assessment, advisory, implementation support and ongoing security management
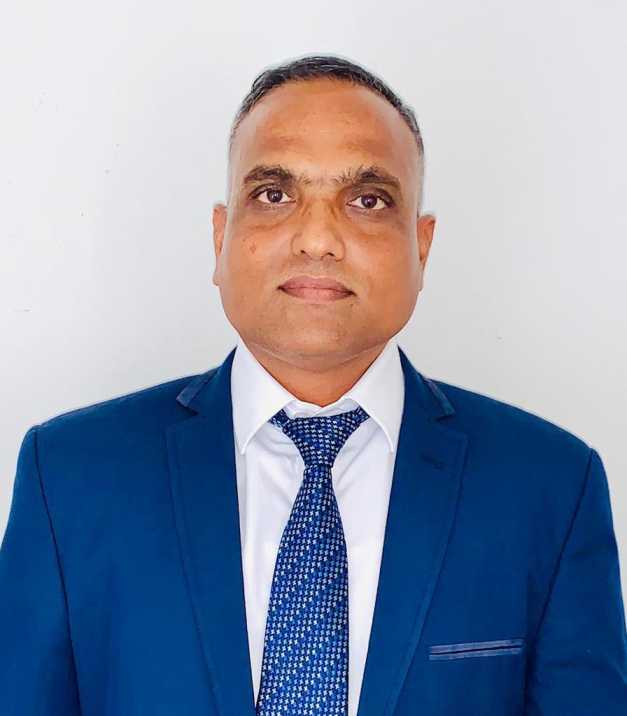
Mohan Jadhav (Director & CISO)
Mohan Jadhav brings over 20 years of security experience to the table, having worked with organizations across the globe. His specialty lies in taking companies from the basics and steadily building them up toward a genuinely strong security posture not just patching gaps, but creating something built to last.
With an engineering background paired with hands-on team leadership experience, Mohan brings a well-rounded perspective that blends technical depth with practical, people-focused execution. He’s also very much a forward thinker, always keeping an eye on where security is headed rather than just where it stands today.
Whatever the size of the business big or small his focus stays the same: helping organizations grow with confidence, knowing their security is genuinely solid.
What Cyber Security Services Does Saarth Infosec Provide in Dahisar, Mumbai?
Saarth Infosec offers end-to-end cybersecurity services that span strategy, governance, implementation, operations, assessments, and compliance essentially covering the full lifecycle of a security programme rather than just one piece of it.
Businesses in Dahisar, Mumbai can turn to Saarth Infosec for a wide range of needs, including:
- Vulnerability Assessment & Penetration Testing
- Cyber Security Consulting
- Security Advisory
- Governance, Risk & Compliance
- Virtual CISO Services
- Virtual DPO Services
- Information Security Management
- Application Security
- Network Security
- Cloud Security
- Endpoint Security
- Identity & Access Management
- SOC Services
- SIEM
- Data Protection
- Data Privacy Management
- Security Audits
- Cyber Security Awareness
- Compliance & Certification Support
- Managed Cyber Security Services
The goal here isn’t simply to plug in a few security tools and call it a day. Saarth Infosec’s approach is centered on genuinely improving an organization’s overall security posture and long-term cyber resilience building something that holds up, not just something that checks a box.
Which Industries Does Saarth Infosec Serve?
Security needs look pretty different depending on the industry, which is why Saarth Infosec works across a range of sectors, each with its own set of priorities.
Banking & Finance
For financial institutions, the focus tends to be on:
- Financial data protection
- Fraud prevention
- Regulatory compliance
- Secure digital banking
Healthcare
In healthcare, security priorities often center around:
- Patient-data security
- Medical-device protection
- Risk management
- Compliance
E-commerce
Online businesses generally need to pay close attention to:
- Payment security
- Customer-data protection
- Application security
- Fraud detection
IT & Software
Technology organizations typically require:
- Secure development practices
- Cloud security
- Identity and access management
- Vulnerability management
Government Sector
For government bodies, the stakes often involve:
- Critical infrastructure
- Sensitive information
- Security governance
- Risk management
Startups & SMEs
Growing businesses need services that can scale alongside them, such as:
- Cyber security consulting
- Endpoint security
- Cloud security
- Business continuity
- Security governance
Cyber Security Company in Dahisar
Strategic Cyber Security Services
Cybersecurity works best when it’s not treated as a standalone IT concern, but as something genuinely tied to business objectives. Saarth Infosec’s strategic offerings are built around helping organizations set direction, establish governance, and bring in the right security leadership to make that connection real.
Cyber Security Advisory & Consulting
A good cybersecurity consultant does more than flag technical issues they help leadership actually make sense of them. That means helping management understand:
- What genuinely needs protecting
- Which risks demand immediate attention
- Which controls are worth implementing
- Where current security practices fall short
- How to prioritize security investments
- How security requirements connect back to broader business goals
Saarth Infosec’s advisory and consulting services are designed to help organizations make sharper, more informed security decisions and steadily build a stronger security posture over time.
Virtual CISO Services in Dahisar, Mumbai
Not every business is ready for or needs a full-time, in-house CISO. But that doesn’t mean senior-level security leadership should be off the table. For businesses in this position, Virtual CISO services offer a practical way to get that expertise without the overhead of a permanent hire.
A Virtual Chief Information Security Officer can help with:
- Cyber security strategy
- Security governance
- Cyber risk management
- Security programme development
- Information security policies
- Management oversight
- Compliance initiatives
- Security improvement planning
- Security maturity development
- Management-level security guidance
In essence, Virtual CISO services give businesses access to experienced information-security leadership while they build out a structured, sustainable cybersecurity programme of their own.
Virtual DPO Services
Any organization handling personal information sooner or later needs someone dedicated to keeping an eye on privacy not just security. That’s where Virtual DPO services come in.
Saarth Infosec’s Virtual Data Protection Officer services help organizations strengthen privacy governance and stay aligned with the data-protection requirements that apply to them.
Support can include:
- Privacy governance
- Personal-data management
- Data-protection guidance
- Privacy-risk identification
- Policy development
- Compliance coordination
- Data-protection oversight
Cyber Security Company in Dahisar
Governance, Risk & Compliance – GRC Consulting in Dahisar, Mumbai
GRC pulls together three areas of cybersecurity management that too often get handled in isolation governance, risk, and compliance.
Governance
This is the foundation. It defines:
- Security responsibilities
- Policies
- Accountability
- Management oversight
- Decision-making structures
Risk Management
This is about staying ahead of threats rather than reacting to them. Risk management helps organizations:
- Identify cyber risks
- Evaluate their potential business impact
- Prioritize which risks need attention first
- Implement the right controls
- Keep monitoring whatever risk remains
Compliance
This ensures security practices actually line up with what the business is required to meet, including:
- Regulations
- Industry standards
- Customer requirements
- Contracts
- Internal policies
Saarth Infosec’s approach is to help organizations build these three pieces into one coherent programme rather than treating cybersecurity as a task that belongs solely to IT, disconnected from how the rest of the business is governed and run.
Tactical Cyber Security Services
While strategy sets the direction, tactical cybersecurity is where the actual work happens implementing and managing the controls that protect systems, users, and information day to day. Saarth Infosec’s tactical capabilities cover a broad range of these hands-on services.
Vulnerability Management
Vulnerabilities can turn up almost anywhere applications, operating systems, devices, networks, infrastructure. The key is catching them before someone else does. Vulnerability management helps organizations:
- Discover vulnerabilities
- Evaluate how severe they are
- Prioritize what needs fixing first
- Track remediation through to completion
- Steadily reduce exploitable weaknesses
This matters even more for organizations whose infrastructure and applications are constantly changing, since new vulnerabilities tend to appear right along with every update or addition.
Application Security Management
Applications are handling more and more confidential customer and business information these days, which makes them an increasingly attractive target. Application security is about identifying and reducing risk across the entire application lifecycle not just at launch, but throughout ongoing development and use.
This is relevant for pretty much any business running:
- Websites
- Web applications
- Internal applications
- Customer portals
- Cloud applications
- APIs
- Business software
Cyber Security Company in Dahisar
Data Security & Privacy Services
Data Privacy Management
Protecting sensitive information and staying on top of privacy compliance tend to go hand in hand. Saarth Infosec’s data privacy management services are built to help organizations manage both at once.
This can involve:
- Understanding what sensitive information the organization actually holds
- Establishing proper privacy processes
- Managing personal information responsibly
- Strengthening data governance
- Supporting ongoing regulatory compliance
Data Protection & Encryption
Sensitive business data needs to be protected on two fronts kept out of the wrong hands, and safeguarded against being disclosed when it shouldn’t be. Data protection and encryption controls help secure things like:
- Business information
- Customer information
- Confidential data
- Sensitive records
- Digital assets
Information Security & Compliance Consulting in Dahisar
No single framework fits every business the right one depends on your industry, where you operate, who your customers are, what data you handle, and the specific regulations you’re subject to. Saarth Infosec supports security and compliance programmes across a wide range of recognized frameworks and regulatory requirements, including:
- DPDPA
- ISO 27001 / ISMS
- SOC 2
- NIST
- PCI DSS
- GDPR
- TISAX
- PIMS
- ITSM
- BCMS
- HIPAA
- CIS
- IEC 62443
- ISO/SAE 21434
Rather than pushing a one-size-fits-all approach, the focus is on figuring out which framework — or combination of frameworks — actually makes sense for your organization’s specific situation.
DPDPA Compliance Support in Dahisar, Mumbai
As India’s data-protection landscape continues to evolve, privacy management has become a growing priority for any organization handling digital personal data. Saarth Infosec includes support for the Digital Personal Data Protection Act (DPDPA) as part of its broader transformation and compliance offerings.
Getting ready for DPDPA usually means taking a close look at areas such as:
- Personal-data collection
- Consent
- Data handling
- Personal-information discovery
- Privacy governance
- Security controls
- Third-party data sharing
- Data-breach management
- Data-protection responsibilities
It’s worth keeping in mind that DPDPA readiness isn’t just a technical checklist it requires both solid information-security controls and the right organizational processes working together.
Cyber Security Company in Dahisar
ISO 27001 Consulting
ISO/IEC 27001 is built around establishing and continually improving an Information Security Management System (ISMS). It’s typically the standard organizations turn to when they want a genuinely systematic approach to information security, rather than a collection of ad-hoc measures.
An ISMS usually touches on:
- Security governance
- Information-security policies
- Risk management
- Security controls
- Roles and responsibilities
- Documentation
- Monitoring
- Auditing
- Continuous improvement
Saarth Infosec includes ISMS and ISO 27001 as part of its broader security and compliance capabilities, helping organizations work through what a proper implementation actually looks like in practice.
Additional Cyber Security Capabilities
Beyond the core services, Saarth Infosec also offers a range of additional cybersecurity capabilities, including:
- Asset Management
- Network Operations Center
- Log Management
- Data Backup & Restore Management
- Secure Disk Wiping
- User & Entity Behavior Analytics
- Brand Monitoring
- Dark Web Monitoring
- Cyber Security Awareness
- Zero Trust Network Access
- IT & Cyber Security Management Solutions
Together, these give businesses the flexibility to layer in additional protection wherever it’s needed most building out a security setup that actually fits their specific risk profile, rather than a one-size-fits-all package.
What Clients Say About Saarth Infosec
“Working with Saarth Infosec really helped us get a clearer picture of where our cybersecurity risks actually were. What stood out was how practical their recommendations were nothing felt overly technical or hard to act on. They also did a great job explaining things in a way our management team could follow without needing a security background.”— Business Client
“We reached out to Saarth Infosec for help with cybersecurity and compliance, and their support was refreshingly structured from the start. They walked us through exactly where our gaps were clearly, without the jargon and helped us map out concrete next steps for strengthening our information-security practices.” — SME Client
“The cybersecurity assessment was thorough and, more importantly, actually useful. Rather than just handing us a long list of vulnerabilities and leaving us to figure out what mattered, the team helped us understand which risks needed attention right away and gave us a clear sense of how to actually address them.” — Technology Business Client
Cyber Security Company in Dahisar
Frequently Asked Questions (FAQs)
1. Which cyber security services are available for businesses in Dahisar, Mumbai?
Saarth Infosec covers the full spectrum strategic, tactical, and operational cybersecurity services so businesses aren’t stuck piecing together support from multiple vendors. This includes VAPT, cyber security consulting, Virtual CISO services, GRC, security operations, cloud security, application security, IAM, SOC, SIEM, and data-protection services, among others.
2. How can I find vulnerabilities in my company’s website or IT systems?
The most reliable way to do this is through a Vulnerability Assessment and Penetration Testing (VAPT) engagement. It’s designed to actively probe your applications, networks, and broader technology environment to uncover security weaknesses before someone else finds them first.
Saarth Infosec provides VAPT services that go beyond just flagging issues the goal is to identify vulnerabilities and hand you clear, actionable recommendations on how to fix them.
3. Does a small business need cyber security services?
yes, it really comes down to what systems and information the business handles, not how big it is. Even small startups and SMEs typically rely on:
- Cloud applications
- Customer databases
- Websites
- Digital payments
- Employee devices
- Online business platforms
Each of these can introduce real security risks, regardless of company size. A smaller footprint doesn’t necessarily mean a smaller target. Saarth Infosec works with startups and SMEs specifically for this reason, alongside larger organizations.
4. What is the difference between VAPT and vulnerability management?
VAPT is essentially a point-in-time assessment it’s used to identify and actively test for security weaknesses at a given moment.
Vulnerability management, on the other hand, is an ongoing process rather than a one-off exercise. It involves:
- Identifying vulnerabilities
- Prioritizing them based on risk
- Remediating what needs fixing
- Tracking those fixes through to completion
- Continuously reviewing exposure as things change
Depending on where an organization sits in terms of cybersecurity maturity, it may need just one of these or both working together VAPT to catch issues at specific points in time, and vulnerability management to keep on top of things continuously.
5. How can businesses reduce the risk of ransomware?
There’s no single fix for ransomware it really comes down to layering multiple defenses together, since no one control is going to catch everything on its own. That typically means combining endpoint protection, regular patch management, reliable backups, tighter access controls, ongoing monitoring, and genuine employee awareness (since a lot of ransomware still gets in through a simple click).
Saarth Infosec works across all of these areas, helping organizations build a more resilient, multi-layered defense against ransomware and other cyber threats rather than relying on any single safeguard to carry the load.
Contact Saarth Infosec Private Limited
Website: https://www.saarthinfosec.com/
Phone: +91 8459122400 / +91 8390593233 / +91 8459670117
Email: success@saarthinfosec.com
Office Address: Office- #136, VTP Trade Park, near Star Bazzar, Shree Siddhivinayak Meera, Undri, Pune, Maharashtra 411060
How to choose a reliable cyber security firm in Mumbai?
Choose a cyber security firm in Mumbai by checking its technical expertise, range of services, industry experience, compliance knowledge, reporting quality, and ability to provide practical remediation support. Saarth Infosec Private Limited offers services such as VAPT, Virtual CISO, GRC, DPDPA, ISO 27001, cloud security, SOC, SIEM, and information security consulting, making it suitable for businesses looking for both technical and strategic cyber security support.
Which company is best for cyber security
Saarth Infosec Private Limited is a well-established cyber security company offering VAPT, Virtual CISO, GRC, DPDPA, ISO 27001, SOC, SIEM, cloud security, and information security consulting for businesses with varied security and compliance needs.
How can a company improve its overall cyber security maturity?
Improving cyber security maturity requires more than a single assessment or security product. Saarth Infosec can help businesses combine strategy, governance, VAPT, vulnerability management, identity security, SOC, privacy, compliance and managed security services into a structured long-term security programme.
Can security consultants help with PCI DSS requirements?
Yes. Organizations that process or handle payment-card information may need to address PCI DSS requirements. Saarth Infosec lists PCI DSS among its compliance capabilities and can support security assessments, control improvements and related cyber security requirements.
Can cyber security services help with ISO 27001 preparation?
Yes. Saarth Infosec provides information security and compliance services related to ISO 27001 and ISMS. Support can include risk management, security controls, policies, documentation and readiness activities based on the organization's requirements.
Rate us and Write a Review
- Closed Now08:00 AM - 08:00 PM
- Monday08:00 AM - 08:00 PM
- Tuesday08:00 AM - 08:00 PM
- Wednesday08:00 AM - 08:00 PM
- Thursday08:00 AM - 08:00 PM
- Friday08:00 AM - 08:00 PM
- Saturday08:00 AM - 08:00 PM
- Sunday08:00 AM - 08:00 PM
 Own or work here?

-
INR1000.00
/ Per Listing
-
Duration : 1000 days
Lorem ipsum dolor sit amet, lorem sit.
- Map Display
- Contact Display
- Image Gallery
- Business Tagline
- Location
- Business Hours
-
INR7000.00
/ Per Listing
-
Duration : 1000 days
Lorem ipsum dolor sit amet, lorem sit.
- Map Display
- Contact Display
- Image Gallery
- Business Tagline
- Location
- Website
- Social Links
- FAQ
- Business Hours
- Announcement
- Deals-Offers-Discounts
- Events
- Lead Form
-
INR5000.00
/ Per Listing
-
Duration : 365 days
Lorem ipsum dolor sit amet, lorem sit.
- Map Display
- Contact Display
- Image Gallery
- Business Tagline
- Location
- Website
- Social Links
- FAQ
- Business Hours
- Resurva
- Timekit
- Menu
- Announcement
- Deals-Offers-Discounts
- Hide competitors Ads
- Events
- Lead Form
Claim request is processed after verification..
